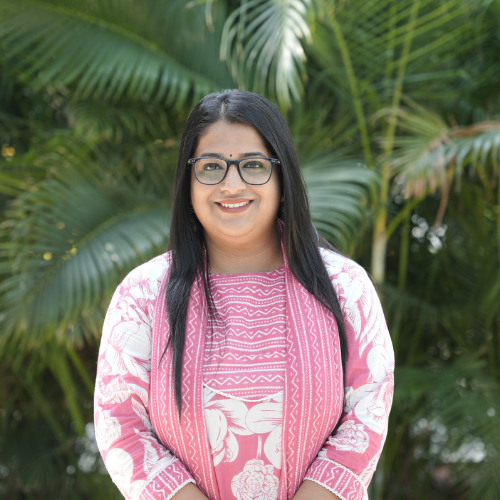
Faculty Ms Anwesha Kashyap

Ms Anwesha Kashyap

Assistant Professor

Department of Computer Science and Engineering

Contact Details

anwesha.k@srmap.edu.in

Office Location

Social Links

Education

2026
PhD (CSE)
IIIT Guwahati, Assam
2021
M.Tech
IIIT Guwahati, Assam
2019
B.Tech
DUIET, Dibrugarh University, Assam

Personal Website

Experience

  • Assistant Professor, SRM University-AP, Andhra Pradesh
  • Teaching Assistant, Indian Institute of Information Technology Guwahati, Assam, India

Research Interest

  • My research interests are Formal Methods, Static Analysis and Verification, Information Flow Security, Database Security, Abstract Interpretation, and Software Engineering, in which I am currently working on developing efficient techniques for the static analysis and verification of database-driven software systems. I am particularly interested in applying Abstract Interpretation and Formal Methods to verify information flow security, detect software vulnerabilities, and improve the correctness, security, and reliability of modern software applications. Beyond my current research, I am interested in exploring emerging research directions at the intersection of Artificial Intelligence, Machine Learning, and Software Engineering, with a focus on intelligent program analysis, AI-assisted software development, automated software testing and verification, secure software engineering, and trustworthy AI-driven software systems.

Memberships

  • IEEE

Publications

  • Refining Dependency Analysis in Database-Driven Programs Using Abstract Interpretation

    Kashyap A., Jana A.

    Conference paper, Lecture Notes in Computer Science, 2026, DOI Link

    View abstract ⏷

    Program Dependency Graphs (PDGs) have been a crucial component of software engineering for many years, enabling numerous activities including program slicing, security analysis, debugging, and optimization of code. Based on this idea, Database-Oriented Program Dependency Graphs (DOPDGs) were conceived to include database statements and their dependency. Nevertheless, the use of syntax-based analysis in DOPDGs can be problematic and even lead to false information and redundant warnings. This paper suggests a semantics-based enhancement of dependency analysis for increased precision and efficiency. Through improved interpretation of dependencies, our approach reduces false positives and provides more reliable results. The effectiveness of this method is demonstrated through benchmark code evaluations.
  • A Semantic Approximation Technique for Automated Detection of Illicit Information Flows in Web-Based Systems

    Kashyap A., Jana A.

    Article, IEEE Access, 2026, DOI Link

    View abstract ⏷

    Security in software systems ultimately seeks to safeguard the confidentiality, integrity, and availability of information. Of these, ensuring confidentiality is extremely difficult as sensitive information can leak due to unauthorized information flows through program logic. These flows typically emerge when confidential values indirectly dictate public variables, enabling an attacker to extract secret information from observable behavior. Traditional controls, such as access control and encryption, protect systems against outside attacks but do not catch these inside propagation-based leaks. Current information flow analysis techniques, including dependency graph-based, have tried to solve this problem; however, they tend to be limited to syntactic analysis, resulting in inaccurate results and high false positives. In this paper, we introduce a security-focused framework that enhances database-driven program confidentiality verification through a dependency graph-based method. The system works in the following steps: (1) the program is converted to an extended dependency graph representation, (2) the syntactic graph is enriched with a semantics-based method based on Abstract Interpretation, (3) all potential information flow paths are discovered from the enriched graph, and (4) each of these paths is examined to identify illegitimate or confidentiality-violating flows. The semantics-based approach uses interval (non-relational) and polyhedral (relational) abstract domains to trade off scalability against accuracy, while sensitivity levels are computed for variables and database fields to enable satisfiability-based verification. The resulting system guarantees sound over-approximation of all potential flows, minimizes false positives, and offers a solid mechanism for guaranteeing information flow security in applications based on data.
  • Static Analysis of Integrity Constraints in Database Applications Using Semantic-Based Approach

    Kashyap A., Jana A.

    Conference paper, 2026 IEEE 15th International Conference on Communication Systems and Network Technologies, CSNT 2026, 2026, DOI Link

    View abstract ⏷

    Accuracy and consistency of data are very important in database systems, particularly with the increasing use of sensitive data. This paper presents a semantic verification approach for database systems that checks the data integrity constraints using abstract interpretation on the octagon abstract domain. The approach abstracts the semantic meaning of SQL statements, enabling the analysis of the numerical relationship between data variables without focusing on syntactic analysis alone. The proposed system can automatically check if the integrity constraints specified by organizational policies are satisfied. The approach is tested on database benchmark applications and proved effective in detecting integrity constraint violations with high accuracy and scalability. In summary, this paper presents an efficient approach for checking integrity properties in complex data-driven systems.
  • A survey: on detection and prevention techniques of SQL injection attacks

    Kashyap A., Jana A.

    Article, International Journal of Information and Computer Security, 2025, DOI Link

    View abstract ⏷

    We are constantly exposed to the extensive usage of online applications in our daily lives. The web application’s backend uses database technology that stores and processes sensitive data. One of the primary concerns of a web application in terms of data security is to safeguard sensitive data in the database. SQL injection attacks are one of the most serious security concerns of web applications (SQLIA). Akamai report suggests that SQLIAs accounted for more than 72% of all web application security attacks in the last five years. Therefore, SQLIA is one of the most severe attacks used against database-driven web applications, which compromises data privacy. It is a code injection type attack where an attacker injects malicious SQL queries to get unauthorised access to the database. Several research proposals have been published to address these security threats. In this paper, we first provide the current state-of-the-art on SQLIA and a comprehensive analysis of SQLIA vulnerabilities, detection and prevention strategies in the literature, as well as a complete comparison evaluation of the various existing methodologies.
  • Illegitimate Data Flow Detection of Data-Driven Applications Using Dependency Graph

    Kashyap A., Jana A.

    Conference paper, IEEE Region 10 Annual International Conference, Proceedings/TENCON, 2025, DOI Link

    View abstract ⏷

    Detecting potential data breaches in software systems can be effectively achieved through language-based information flow security analysis. Significant risk to confidential data, potentially leading to security breaches, is posed because of poor coding practices in database applications. To tackle the issue, our paper presents a dependency graphbased approach that identifies potential confidentiality leaks in software code. For a variety of software engineering tasks, including information flow security analysis, debugging, code optimization, enabling code reuse, and enhancing program comprehension, Dependency information plays an essential role. Existing dependency information techniques fail to generate precise results. Through the utilisation of syntaxbased dependency analysis, we enhance and improvise on existing techniques by introducing a new Dependency, which can result in indirect information leakage. A precise dependency information, which improves the accuracy of security analysis results, is provided through this refinement. We provide experimental results on benchmark codes to validate our approach. To determine illegal information flows, we use propositional formulae for the security-level truth assignments. Thorough utilisation of such an approach aids in bridging the gap between existing approaches and future applications to handle the same.
  • Analysis of Illegitimate Information Flows in Web-based System by Semantic Approximation

    Kashyap A., Jana A.

    Conference paper, International Symposium on Advanced Networks and Telecommunication Systems, ANTS, 2025, DOI Link

    View abstract ⏷

    In order to guarantee the confidentiality of sensitive information in software systems, strong mechanisms for identifying probable security violations are required. Language-oriented information flow analysis can be a strong mechanism that identifies vulnerabilities resulting from insecure coding techniques, especially web-based applications. To address this issue, we introduce a dependency graph-based framework to identify potential confidentiality violations present in source code. The examination of dependencies is important in a number of software engineering tasks, such as debugging, code optimization, support for component reuse, improving code readability, and, most importantly, protecting information flow. Traditional methods of dependency information extraction are not always precise enough to provide sound security assessments. To counter this limitation, we enhance the analysis process by considering both Direct and Indirect Dependencies. The improved method enables more thorough and precise mapping of dependencies, thus making security assessments more reliable. We validate our method through mathematical proofs. To systematically detect unauthorized information flows, we utilize propositional logic-based formulations corresponding to predetermined security-level constraints. Our research aims to bridge the gap between the existing requirements of secure software development processes and the analytical approaches that are now accessible by utilising this refined approach.
  • A Static Analysis Approach to Verify Data Integrity of Web-based Software Systems

    Kashyap A., Jana A.

    Conference paper, International Symposium on Advanced Networks and Telecommunication Systems, ANTS, 2024, DOI Link

    View abstract ⏷

    Web-based application plays an important role in our day-to-day activities. Such kinds of applications deal with large volumes of data access and data manipulation continuously. Data security is one of the prime concerns for data access. During any operation on data, it is important to preserve the data integrity to maintain security. In this work, we provide a static analysis approach to verify data integrity to ensure the data security of web-based applications. We used an abstract-based static analysis technique with the help of the powerset domain of interval to analyze the actual behavior of the system.
  • Extending Semantic based Techniques for Policy-based Slicing of Database Program

    Kashyap A., Jana A.

    Article, International Journal of Computer Information Systems and Industrial Management Applications, 2023,

    View abstract ⏷

    The innovation of the program slicing technique brings a revolution to address several issues (e.g. code understanding, debugging, maintenance, testing, etc.) in the more complex and large information systems. Over the past, many slicing techniques have been proposed, however, all these existing approaches did not consider the external database states. Moreover, the majority of the proposed slicing approaches are syntax-based and they do not consider the properties of variables and database attributes. Therefore, existing techniques are not directly applicable to data-intensive programs in information system scenarios and majority of them fails to compute precise slicing results. In this work, we propose a policy-based slicing framework for data-intensive programs. The policies are integrity constraints that are defined on data as per the business goal and kept in a backend database. We design our propose framework using the data dependency graph of data-intensive programs. We refine (by removing false alarms) the data dependency graph using semantics-based techniques, Condition-Action Rules and Hoare Logic. This refined graph yields precise slicing results w.r.t the policies of data-intensive programs.
  • Policy-Based Code Slicing of Database Application Using Semantic Rule-Based Approach

    Kashyap A., Jana A.

    Conference paper, Lecture Notes in Networks and Systems, 2023, DOI Link

    View abstract ⏷

    We introduce a policy-based slicing of database application. The policies are defined on data, that is kept in a backend database. The majority of the proposed slicing approaches are syntax-based and they do not consider the properties of variables and database-attributes. Therefore the existing approaches unable to compute precise slicing result. In this work, we refine (by removing false alarms) dependency graph using semantics-based technique. We formalize the data dependencies among various statements using semantics rule based approach and perform emptiness checking to identify the false alarm. This refined graph yields precise slicing results w.r.t the policies of a database application.
  • Integrity Constraint Verification of Structured Query Language by Abstract Interpretation

    Kashyap A., Jana A.

    Conference paper, Proceedings - 2022 OITS International Conference on Information Technology, OCIT 2022, 2022, DOI Link

    View abstract ⏷

    Over the decades and now-a-days the data-driven applications are playing a pivotal role in every aspect of our daily lives by providing an easy interface to store, access and process crucial data with the help of Database Management System (DBMS). However, it is always necessary to ensure the data integrity for every operation on a database. In this paper, we propose a novel framework for Structured Query Language (SQL), aiming at automatically and formally verifying integrity constraints in terms of enterprise policy specifications on data in the underlying database. To this aim, we extend the abstract interpretation theory to the case of structured query languages.
  • Confidentiality Leakage Analysis of Database-Driven Applications

    Jana A., Kashyap A.

    Conference paper, Communications in Computer and Information Science, 2021, DOI Link

    View abstract ⏷

    In a software system the database technology is one of the most important part that stores external information into the permanent storage and process them accordingly. However, the most prime concern of any information system is to protect the data in the persistent storage from any unauthorised access. Sometimes, the database technology is developed in such a way that sensitive information may be leaked directly or indirectly during information processing along with control structure of a software code. In this paper, we propose a dependency graph based approach to identify possible confidentiality leakage of a software code. We design a framework using the semantic based dependency analysis technique. It refines the existing syntax-based dependency graph by removing false alarms and generates more precise dependency information that leads to improved security analysis results.

Patents

Projects

Scholars

Interests

  • Abstract Interpretation
  • Database Security
  • Formal Methods
  • Information Flow Security
  • Software Engineering
  • Static Analysis and Verification

Thought Leaderships

There are no Thought Leaderships associated with this faculty.

Top Achievements

Research Area

No research areas found for this faculty.

Computer Science and Engineering is a fast-evolving discipline and this is an exciting time to become a Computer Scientist!

Computer Science and Engineering is a fast-evolving discipline and this is an exciting time to become a Computer Scientist!

Recent Updates

No recent updates found.

Education
2019
B.Tech
DUIET, Dibrugarh University
2021
M.Tech
IIIT Guwahati
2026
PhD (CSE)
IIIT Guwahati
Experience
  • Assistant Professor, SRM University-AP, Andhra Pradesh
  • Teaching Assistant, Indian Institute of Information Technology Guwahati, Assam, India
Research Interests
  • My research interests are Formal Methods, Static Analysis and Verification, Information Flow Security, Database Security, Abstract Interpretation, and Software Engineering, in which I am currently working on developing efficient techniques for the static analysis and verification of database-driven software systems. I am particularly interested in applying Abstract Interpretation and Formal Methods to verify information flow security, detect software vulnerabilities, and improve the correctness, security, and reliability of modern software applications. Beyond my current research, I am interested in exploring emerging research directions at the intersection of Artificial Intelligence, Machine Learning, and Software Engineering, with a focus on intelligent program analysis, AI-assisted software development, automated software testing and verification, secure software engineering, and trustworthy AI-driven software systems.
Awards & Fellowships
Memberships
  • IEEE
Publications
  • Refining Dependency Analysis in Database-Driven Programs Using Abstract Interpretation

    Kashyap A., Jana A.

    Conference paper, Lecture Notes in Computer Science, 2026, DOI Link

    View abstract ⏷

    Program Dependency Graphs (PDGs) have been a crucial component of software engineering for many years, enabling numerous activities including program slicing, security analysis, debugging, and optimization of code. Based on this idea, Database-Oriented Program Dependency Graphs (DOPDGs) were conceived to include database statements and their dependency. Nevertheless, the use of syntax-based analysis in DOPDGs can be problematic and even lead to false information and redundant warnings. This paper suggests a semantics-based enhancement of dependency analysis for increased precision and efficiency. Through improved interpretation of dependencies, our approach reduces false positives and provides more reliable results. The effectiveness of this method is demonstrated through benchmark code evaluations.
  • A Semantic Approximation Technique for Automated Detection of Illicit Information Flows in Web-Based Systems

    Kashyap A., Jana A.

    Article, IEEE Access, 2026, DOI Link

    View abstract ⏷

    Security in software systems ultimately seeks to safeguard the confidentiality, integrity, and availability of information. Of these, ensuring confidentiality is extremely difficult as sensitive information can leak due to unauthorized information flows through program logic. These flows typically emerge when confidential values indirectly dictate public variables, enabling an attacker to extract secret information from observable behavior. Traditional controls, such as access control and encryption, protect systems against outside attacks but do not catch these inside propagation-based leaks. Current information flow analysis techniques, including dependency graph-based, have tried to solve this problem; however, they tend to be limited to syntactic analysis, resulting in inaccurate results and high false positives. In this paper, we introduce a security-focused framework that enhances database-driven program confidentiality verification through a dependency graph-based method. The system works in the following steps: (1) the program is converted to an extended dependency graph representation, (2) the syntactic graph is enriched with a semantics-based method based on Abstract Interpretation, (3) all potential information flow paths are discovered from the enriched graph, and (4) each of these paths is examined to identify illegitimate or confidentiality-violating flows. The semantics-based approach uses interval (non-relational) and polyhedral (relational) abstract domains to trade off scalability against accuracy, while sensitivity levels are computed for variables and database fields to enable satisfiability-based verification. The resulting system guarantees sound over-approximation of all potential flows, minimizes false positives, and offers a solid mechanism for guaranteeing information flow security in applications based on data.
  • Static Analysis of Integrity Constraints in Database Applications Using Semantic-Based Approach

    Kashyap A., Jana A.

    Conference paper, 2026 IEEE 15th International Conference on Communication Systems and Network Technologies, CSNT 2026, 2026, DOI Link

    View abstract ⏷

    Accuracy and consistency of data are very important in database systems, particularly with the increasing use of sensitive data. This paper presents a semantic verification approach for database systems that checks the data integrity constraints using abstract interpretation on the octagon abstract domain. The approach abstracts the semantic meaning of SQL statements, enabling the analysis of the numerical relationship between data variables without focusing on syntactic analysis alone. The proposed system can automatically check if the integrity constraints specified by organizational policies are satisfied. The approach is tested on database benchmark applications and proved effective in detecting integrity constraint violations with high accuracy and scalability. In summary, this paper presents an efficient approach for checking integrity properties in complex data-driven systems.
  • A survey: on detection and prevention techniques of SQL injection attacks

    Kashyap A., Jana A.

    Article, International Journal of Information and Computer Security, 2025, DOI Link

    View abstract ⏷

    We are constantly exposed to the extensive usage of online applications in our daily lives. The web application’s backend uses database technology that stores and processes sensitive data. One of the primary concerns of a web application in terms of data security is to safeguard sensitive data in the database. SQL injection attacks are one of the most serious security concerns of web applications (SQLIA). Akamai report suggests that SQLIAs accounted for more than 72% of all web application security attacks in the last five years. Therefore, SQLIA is one of the most severe attacks used against database-driven web applications, which compromises data privacy. It is a code injection type attack where an attacker injects malicious SQL queries to get unauthorised access to the database. Several research proposals have been published to address these security threats. In this paper, we first provide the current state-of-the-art on SQLIA and a comprehensive analysis of SQLIA vulnerabilities, detection and prevention strategies in the literature, as well as a complete comparison evaluation of the various existing methodologies.
  • Illegitimate Data Flow Detection of Data-Driven Applications Using Dependency Graph

    Kashyap A., Jana A.

    Conference paper, IEEE Region 10 Annual International Conference, Proceedings/TENCON, 2025, DOI Link

    View abstract ⏷

    Detecting potential data breaches in software systems can be effectively achieved through language-based information flow security analysis. Significant risk to confidential data, potentially leading to security breaches, is posed because of poor coding practices in database applications. To tackle the issue, our paper presents a dependency graphbased approach that identifies potential confidentiality leaks in software code. For a variety of software engineering tasks, including information flow security analysis, debugging, code optimization, enabling code reuse, and enhancing program comprehension, Dependency information plays an essential role. Existing dependency information techniques fail to generate precise results. Through the utilisation of syntaxbased dependency analysis, we enhance and improvise on existing techniques by introducing a new Dependency, which can result in indirect information leakage. A precise dependency information, which improves the accuracy of security analysis results, is provided through this refinement. We provide experimental results on benchmark codes to validate our approach. To determine illegal information flows, we use propositional formulae for the security-level truth assignments. Thorough utilisation of such an approach aids in bridging the gap between existing approaches and future applications to handle the same.
  • Analysis of Illegitimate Information Flows in Web-based System by Semantic Approximation

    Kashyap A., Jana A.

    Conference paper, International Symposium on Advanced Networks and Telecommunication Systems, ANTS, 2025, DOI Link

    View abstract ⏷

    In order to guarantee the confidentiality of sensitive information in software systems, strong mechanisms for identifying probable security violations are required. Language-oriented information flow analysis can be a strong mechanism that identifies vulnerabilities resulting from insecure coding techniques, especially web-based applications. To address this issue, we introduce a dependency graph-based framework to identify potential confidentiality violations present in source code. The examination of dependencies is important in a number of software engineering tasks, such as debugging, code optimization, support for component reuse, improving code readability, and, most importantly, protecting information flow. Traditional methods of dependency information extraction are not always precise enough to provide sound security assessments. To counter this limitation, we enhance the analysis process by considering both Direct and Indirect Dependencies. The improved method enables more thorough and precise mapping of dependencies, thus making security assessments more reliable. We validate our method through mathematical proofs. To systematically detect unauthorized information flows, we utilize propositional logic-based formulations corresponding to predetermined security-level constraints. Our research aims to bridge the gap between the existing requirements of secure software development processes and the analytical approaches that are now accessible by utilising this refined approach.
  • A Static Analysis Approach to Verify Data Integrity of Web-based Software Systems

    Kashyap A., Jana A.

    Conference paper, International Symposium on Advanced Networks and Telecommunication Systems, ANTS, 2024, DOI Link

    View abstract ⏷

    Web-based application plays an important role in our day-to-day activities. Such kinds of applications deal with large volumes of data access and data manipulation continuously. Data security is one of the prime concerns for data access. During any operation on data, it is important to preserve the data integrity to maintain security. In this work, we provide a static analysis approach to verify data integrity to ensure the data security of web-based applications. We used an abstract-based static analysis technique with the help of the powerset domain of interval to analyze the actual behavior of the system.
  • Extending Semantic based Techniques for Policy-based Slicing of Database Program

    Kashyap A., Jana A.

    Article, International Journal of Computer Information Systems and Industrial Management Applications, 2023,

    View abstract ⏷

    The innovation of the program slicing technique brings a revolution to address several issues (e.g. code understanding, debugging, maintenance, testing, etc.) in the more complex and large information systems. Over the past, many slicing techniques have been proposed, however, all these existing approaches did not consider the external database states. Moreover, the majority of the proposed slicing approaches are syntax-based and they do not consider the properties of variables and database attributes. Therefore, existing techniques are not directly applicable to data-intensive programs in information system scenarios and majority of them fails to compute precise slicing results. In this work, we propose a policy-based slicing framework for data-intensive programs. The policies are integrity constraints that are defined on data as per the business goal and kept in a backend database. We design our propose framework using the data dependency graph of data-intensive programs. We refine (by removing false alarms) the data dependency graph using semantics-based techniques, Condition-Action Rules and Hoare Logic. This refined graph yields precise slicing results w.r.t the policies of data-intensive programs.
  • Policy-Based Code Slicing of Database Application Using Semantic Rule-Based Approach

    Kashyap A., Jana A.

    Conference paper, Lecture Notes in Networks and Systems, 2023, DOI Link

    View abstract ⏷

    We introduce a policy-based slicing of database application. The policies are defined on data, that is kept in a backend database. The majority of the proposed slicing approaches are syntax-based and they do not consider the properties of variables and database-attributes. Therefore the existing approaches unable to compute precise slicing result. In this work, we refine (by removing false alarms) dependency graph using semantics-based technique. We formalize the data dependencies among various statements using semantics rule based approach and perform emptiness checking to identify the false alarm. This refined graph yields precise slicing results w.r.t the policies of a database application.
  • Integrity Constraint Verification of Structured Query Language by Abstract Interpretation

    Kashyap A., Jana A.

    Conference paper, Proceedings - 2022 OITS International Conference on Information Technology, OCIT 2022, 2022, DOI Link

    View abstract ⏷

    Over the decades and now-a-days the data-driven applications are playing a pivotal role in every aspect of our daily lives by providing an easy interface to store, access and process crucial data with the help of Database Management System (DBMS). However, it is always necessary to ensure the data integrity for every operation on a database. In this paper, we propose a novel framework for Structured Query Language (SQL), aiming at automatically and formally verifying integrity constraints in terms of enterprise policy specifications on data in the underlying database. To this aim, we extend the abstract interpretation theory to the case of structured query languages.
  • Confidentiality Leakage Analysis of Database-Driven Applications

    Jana A., Kashyap A.

    Conference paper, Communications in Computer and Information Science, 2021, DOI Link

    View abstract ⏷

    In a software system the database technology is one of the most important part that stores external information into the permanent storage and process them accordingly. However, the most prime concern of any information system is to protect the data in the persistent storage from any unauthorised access. Sometimes, the database technology is developed in such a way that sensitive information may be leaked directly or indirectly during information processing along with control structure of a software code. In this paper, we propose a dependency graph based approach to identify possible confidentiality leakage of a software code. We design a framework using the semantic based dependency analysis technique. It refines the existing syntax-based dependency graph by removing false alarms and generates more precise dependency information that leads to improved security analysis results.
Contact Details

anwesha.k@srmap.edu.in

Scholars
Interests

  • Abstract Interpretation
  • Database Security
  • Formal Methods
  • Information Flow Security
  • Software Engineering
  • Static Analysis and Verification

Education
2019
B.Tech
DUIET, Dibrugarh University
2021
M.Tech
IIIT Guwahati
2026
PhD (CSE)
IIIT Guwahati
Experience
  • Assistant Professor, SRM University-AP, Andhra Pradesh
  • Teaching Assistant, Indian Institute of Information Technology Guwahati, Assam, India
Research Interests
  • My research interests are Formal Methods, Static Analysis and Verification, Information Flow Security, Database Security, Abstract Interpretation, and Software Engineering, in which I am currently working on developing efficient techniques for the static analysis and verification of database-driven software systems. I am particularly interested in applying Abstract Interpretation and Formal Methods to verify information flow security, detect software vulnerabilities, and improve the correctness, security, and reliability of modern software applications. Beyond my current research, I am interested in exploring emerging research directions at the intersection of Artificial Intelligence, Machine Learning, and Software Engineering, with a focus on intelligent program analysis, AI-assisted software development, automated software testing and verification, secure software engineering, and trustworthy AI-driven software systems.
Awards & Fellowships
Memberships
  • IEEE
Publications
  • Refining Dependency Analysis in Database-Driven Programs Using Abstract Interpretation

    Kashyap A., Jana A.

    Conference paper, Lecture Notes in Computer Science, 2026, DOI Link

    View abstract ⏷

    Program Dependency Graphs (PDGs) have been a crucial component of software engineering for many years, enabling numerous activities including program slicing, security analysis, debugging, and optimization of code. Based on this idea, Database-Oriented Program Dependency Graphs (DOPDGs) were conceived to include database statements and their dependency. Nevertheless, the use of syntax-based analysis in DOPDGs can be problematic and even lead to false information and redundant warnings. This paper suggests a semantics-based enhancement of dependency analysis for increased precision and efficiency. Through improved interpretation of dependencies, our approach reduces false positives and provides more reliable results. The effectiveness of this method is demonstrated through benchmark code evaluations.
  • A Semantic Approximation Technique for Automated Detection of Illicit Information Flows in Web-Based Systems

    Kashyap A., Jana A.

    Article, IEEE Access, 2026, DOI Link

    View abstract ⏷

    Security in software systems ultimately seeks to safeguard the confidentiality, integrity, and availability of information. Of these, ensuring confidentiality is extremely difficult as sensitive information can leak due to unauthorized information flows through program logic. These flows typically emerge when confidential values indirectly dictate public variables, enabling an attacker to extract secret information from observable behavior. Traditional controls, such as access control and encryption, protect systems against outside attacks but do not catch these inside propagation-based leaks. Current information flow analysis techniques, including dependency graph-based, have tried to solve this problem; however, they tend to be limited to syntactic analysis, resulting in inaccurate results and high false positives. In this paper, we introduce a security-focused framework that enhances database-driven program confidentiality verification through a dependency graph-based method. The system works in the following steps: (1) the program is converted to an extended dependency graph representation, (2) the syntactic graph is enriched with a semantics-based method based on Abstract Interpretation, (3) all potential information flow paths are discovered from the enriched graph, and (4) each of these paths is examined to identify illegitimate or confidentiality-violating flows. The semantics-based approach uses interval (non-relational) and polyhedral (relational) abstract domains to trade off scalability against accuracy, while sensitivity levels are computed for variables and database fields to enable satisfiability-based verification. The resulting system guarantees sound over-approximation of all potential flows, minimizes false positives, and offers a solid mechanism for guaranteeing information flow security in applications based on data.
  • Static Analysis of Integrity Constraints in Database Applications Using Semantic-Based Approach

    Kashyap A., Jana A.

    Conference paper, 2026 IEEE 15th International Conference on Communication Systems and Network Technologies, CSNT 2026, 2026, DOI Link

    View abstract ⏷

    Accuracy and consistency of data are very important in database systems, particularly with the increasing use of sensitive data. This paper presents a semantic verification approach for database systems that checks the data integrity constraints using abstract interpretation on the octagon abstract domain. The approach abstracts the semantic meaning of SQL statements, enabling the analysis of the numerical relationship between data variables without focusing on syntactic analysis alone. The proposed system can automatically check if the integrity constraints specified by organizational policies are satisfied. The approach is tested on database benchmark applications and proved effective in detecting integrity constraint violations with high accuracy and scalability. In summary, this paper presents an efficient approach for checking integrity properties in complex data-driven systems.
  • A survey: on detection and prevention techniques of SQL injection attacks

    Kashyap A., Jana A.

    Article, International Journal of Information and Computer Security, 2025, DOI Link

    View abstract ⏷

    We are constantly exposed to the extensive usage of online applications in our daily lives. The web application’s backend uses database technology that stores and processes sensitive data. One of the primary concerns of a web application in terms of data security is to safeguard sensitive data in the database. SQL injection attacks are one of the most serious security concerns of web applications (SQLIA). Akamai report suggests that SQLIAs accounted for more than 72% of all web application security attacks in the last five years. Therefore, SQLIA is one of the most severe attacks used against database-driven web applications, which compromises data privacy. It is a code injection type attack where an attacker injects malicious SQL queries to get unauthorised access to the database. Several research proposals have been published to address these security threats. In this paper, we first provide the current state-of-the-art on SQLIA and a comprehensive analysis of SQLIA vulnerabilities, detection and prevention strategies in the literature, as well as a complete comparison evaluation of the various existing methodologies.
  • Illegitimate Data Flow Detection of Data-Driven Applications Using Dependency Graph

    Kashyap A., Jana A.

    Conference paper, IEEE Region 10 Annual International Conference, Proceedings/TENCON, 2025, DOI Link

    View abstract ⏷

    Detecting potential data breaches in software systems can be effectively achieved through language-based information flow security analysis. Significant risk to confidential data, potentially leading to security breaches, is posed because of poor coding practices in database applications. To tackle the issue, our paper presents a dependency graphbased approach that identifies potential confidentiality leaks in software code. For a variety of software engineering tasks, including information flow security analysis, debugging, code optimization, enabling code reuse, and enhancing program comprehension, Dependency information plays an essential role. Existing dependency information techniques fail to generate precise results. Through the utilisation of syntaxbased dependency analysis, we enhance and improvise on existing techniques by introducing a new Dependency, which can result in indirect information leakage. A precise dependency information, which improves the accuracy of security analysis results, is provided through this refinement. We provide experimental results on benchmark codes to validate our approach. To determine illegal information flows, we use propositional formulae for the security-level truth assignments. Thorough utilisation of such an approach aids in bridging the gap between existing approaches and future applications to handle the same.
  • Analysis of Illegitimate Information Flows in Web-based System by Semantic Approximation

    Kashyap A., Jana A.

    Conference paper, International Symposium on Advanced Networks and Telecommunication Systems, ANTS, 2025, DOI Link

    View abstract ⏷

    In order to guarantee the confidentiality of sensitive information in software systems, strong mechanisms for identifying probable security violations are required. Language-oriented information flow analysis can be a strong mechanism that identifies vulnerabilities resulting from insecure coding techniques, especially web-based applications. To address this issue, we introduce a dependency graph-based framework to identify potential confidentiality violations present in source code. The examination of dependencies is important in a number of software engineering tasks, such as debugging, code optimization, support for component reuse, improving code readability, and, most importantly, protecting information flow. Traditional methods of dependency information extraction are not always precise enough to provide sound security assessments. To counter this limitation, we enhance the analysis process by considering both Direct and Indirect Dependencies. The improved method enables more thorough and precise mapping of dependencies, thus making security assessments more reliable. We validate our method through mathematical proofs. To systematically detect unauthorized information flows, we utilize propositional logic-based formulations corresponding to predetermined security-level constraints. Our research aims to bridge the gap between the existing requirements of secure software development processes and the analytical approaches that are now accessible by utilising this refined approach.
  • A Static Analysis Approach to Verify Data Integrity of Web-based Software Systems

    Kashyap A., Jana A.

    Conference paper, International Symposium on Advanced Networks and Telecommunication Systems, ANTS, 2024, DOI Link

    View abstract ⏷

    Web-based application plays an important role in our day-to-day activities. Such kinds of applications deal with large volumes of data access and data manipulation continuously. Data security is one of the prime concerns for data access. During any operation on data, it is important to preserve the data integrity to maintain security. In this work, we provide a static analysis approach to verify data integrity to ensure the data security of web-based applications. We used an abstract-based static analysis technique with the help of the powerset domain of interval to analyze the actual behavior of the system.
  • Extending Semantic based Techniques for Policy-based Slicing of Database Program

    Kashyap A., Jana A.

    Article, International Journal of Computer Information Systems and Industrial Management Applications, 2023,

    View abstract ⏷

    The innovation of the program slicing technique brings a revolution to address several issues (e.g. code understanding, debugging, maintenance, testing, etc.) in the more complex and large information systems. Over the past, many slicing techniques have been proposed, however, all these existing approaches did not consider the external database states. Moreover, the majority of the proposed slicing approaches are syntax-based and they do not consider the properties of variables and database attributes. Therefore, existing techniques are not directly applicable to data-intensive programs in information system scenarios and majority of them fails to compute precise slicing results. In this work, we propose a policy-based slicing framework for data-intensive programs. The policies are integrity constraints that are defined on data as per the business goal and kept in a backend database. We design our propose framework using the data dependency graph of data-intensive programs. We refine (by removing false alarms) the data dependency graph using semantics-based techniques, Condition-Action Rules and Hoare Logic. This refined graph yields precise slicing results w.r.t the policies of data-intensive programs.
  • Policy-Based Code Slicing of Database Application Using Semantic Rule-Based Approach

    Kashyap A., Jana A.

    Conference paper, Lecture Notes in Networks and Systems, 2023, DOI Link

    View abstract ⏷

    We introduce a policy-based slicing of database application. The policies are defined on data, that is kept in a backend database. The majority of the proposed slicing approaches are syntax-based and they do not consider the properties of variables and database-attributes. Therefore the existing approaches unable to compute precise slicing result. In this work, we refine (by removing false alarms) dependency graph using semantics-based technique. We formalize the data dependencies among various statements using semantics rule based approach and perform emptiness checking to identify the false alarm. This refined graph yields precise slicing results w.r.t the policies of a database application.
  • Integrity Constraint Verification of Structured Query Language by Abstract Interpretation

    Kashyap A., Jana A.

    Conference paper, Proceedings - 2022 OITS International Conference on Information Technology, OCIT 2022, 2022, DOI Link

    View abstract ⏷

    Over the decades and now-a-days the data-driven applications are playing a pivotal role in every aspect of our daily lives by providing an easy interface to store, access and process crucial data with the help of Database Management System (DBMS). However, it is always necessary to ensure the data integrity for every operation on a database. In this paper, we propose a novel framework for Structured Query Language (SQL), aiming at automatically and formally verifying integrity constraints in terms of enterprise policy specifications on data in the underlying database. To this aim, we extend the abstract interpretation theory to the case of structured query languages.
  • Confidentiality Leakage Analysis of Database-Driven Applications

    Jana A., Kashyap A.

    Conference paper, Communications in Computer and Information Science, 2021, DOI Link

    View abstract ⏷

    In a software system the database technology is one of the most important part that stores external information into the permanent storage and process them accordingly. However, the most prime concern of any information system is to protect the data in the persistent storage from any unauthorised access. Sometimes, the database technology is developed in such a way that sensitive information may be leaked directly or indirectly during information processing along with control structure of a software code. In this paper, we propose a dependency graph based approach to identify possible confidentiality leakage of a software code. We design a framework using the semantic based dependency analysis technique. It refines the existing syntax-based dependency graph by removing false alarms and generates more precise dependency information that leads to improved security analysis results.
Contact Details

anwesha.k@srmap.edu.in

Scholars