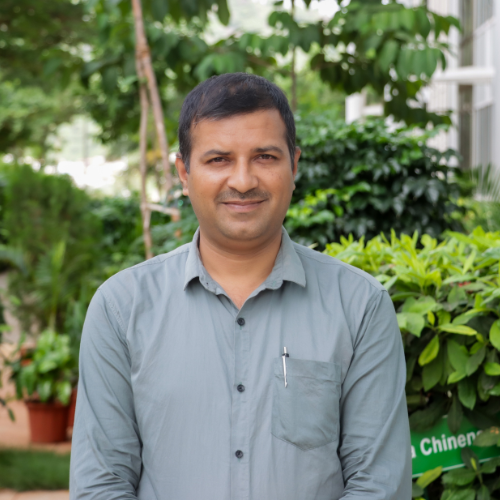
Faculty Dr Raju Gudla
Dr Gudla Raju

Dr Raju Gudla

Assistant professor

Department of Computer Science and Engineering

Contact Details

raju.gu@srmap.edu.in

Office Location

New Academic Block, Level 3, Cubicle No: 11

Social Links

Education

2025
PhD
IIIT Naya Raipur, Chhattissgarh
India
2014
M.Tech
JNTU Hyderabad, Telangana
India
2009
B.Tech
Kakatiya University, Warangal, Telangana, Telangana
India

Personal Website

Experience

  • SRM University-AP, Andhra Pradesh
  • Assistant Professor, Department of CSE, Sri Indu Institute of Engineering and Technology, Hyderabad, Telangana
  • Assistant Professor, Department of CSE, Vaagdevi Engineering College, Warangal Telangana

Research Interest

  • Computer Networks, AI, ML, Quantuam Communications, WSN

Memberships

  • Senior Member IEEE

Publications

  • TCC: Time constrained classification of VPN and non-VPN traffic using machine learning algorithms

    Gudla R., Vollala S., Srinivasa K.G., Amin R.

    Article, Wireless Networks, 2025, DOI Link

    View abstract ⏷

    Accurate traffic classification plays an important role in efficient utilization of network resources, quality of service, and overall management of the network. The identification of virtual private network (VPN) traffic, in particular, is important since it allows distinguishing between encrypted and non-encrypted traffic by VPN service, which is critical for security monitoring, traffic shaping, and the detection of possible misuse of network resources. VPNs are secure, encrypted connections over an insecure network with predetermined protocols; hence, through traditional methods, it is quite challenging to recognize the traffic pattern. This work introduces the time constrained classification (TCC) model, which use a decision tree classification algorithm with autoencoder dimensionality reduction to extract the key features from encrypted VPN traffic. The TCC model accurately classify VPN traffic from non-VPN traffic without degrading performance and limited amount of time. This approach optimizes the classification time for both binary and multi-class VPN and non-VPN traffic. Experimental results show that the decision tree-based autoencoder model achieves a recall score of 0.993 for multi-class classification in 1.8 s on the UNB ISCX VPN-nonVPN dataset (ISCXVPN2016), outperforming state-of-the-art methods while significantly reducing classification time.
  • Detectify: Leveraging Isolation Forest and K-Means for Optimized Network Traffic Anomaly Detection

    Gudla R., Vollala S., Ekka A., Ray S., Amin R.

    Conference paper, 2025 International Conference on Networks and Cryptology, NETCRYPT 2025, 2025, DOI Link

    View abstract ⏷

    Network security is the most essential aspect in today's world, that is, always being digitally connected, and being able to recognize abnormalities is important for defending against cyber attacks. Because regular security systems are not adequate for selective complex infiltrations, this often leads to the development of advanced machine learning models that will supplement the usual anomaly detection capabilities. Network intrusion has been evaluated using algorithms based on NSLKDD dataset that is commonly utilized as a yardstick. However, this study fills this gap, producing effective as well as reliable anomaly detection systems. We preprocessed the data in a comprehensive manner, chose features and used advanced methods like Isolation Forest, K-Means clustering, and Synthetic Minority Over-sampling Technique (SMOTE) in order to improve the quality of logistic regression, k-nearest neighbors and random forest performance through traditional models. Our findings prove much better in detection giving 99.33% accuracy. This means our proposed methodology is good at spotting threats and doing something about them. Application of Isolation Forest technique in anomalous traffic detection has brought unimaginable improvements in separating the two types of networks: legitimate one and malicious ones. The aforementioned is evidenced by our advanced models consistently outshining traditional methods, indicating that these techniques have the potential to strengthen network security against the growing threats of cybercrime through the amalgamation of K-Means clustering and SMOTE algorithms. Our sophisticated models have continued to surpass conventional methods, showcasing the versatility of these techniques in enhancing network security against emerging cyber threats.
  • A novel approach for classification of Tor and non-Tor traffic using efficient feature selection methods

    Gudla R., Vollala S., Srinivasa K.G., Amin R.

    Article, Expert Systems with Applications, 2024, DOI Link

    View abstract ⏷

    In the dynamic realm of encrypted communications, traffic analysis and its classification are crucial for efficient resource utilization and network management. The prevalence of encryption technologies, The Onion Router (Tor) a globally recognized privacy-preserving network, poses a challenge for the task at hand by introducing complexity through its innovative onion routing mechanism. To overcome Tor's limitations not only in terms of achieving better accuracy but also in performing classification in time-constrained scenarios, we propose a classification approach for Tor and non-Tor traffic classification, utilizing multiple models to enhance categorization and application identification. Leveraging the University of New Brunswick (UNB) Tor and non-Tor dataset, initially in a packet capture format, the preprocessing is done by transforming through CICFlowmeter. To expedite classification, we applied feature selection techniques like Principal Component Analysis (PCA) and t-Distributed Stochastic Neighbor Embedding (tSNE). Machine learning algorithms like support vector machine (SVM), Gradient Boosting, Random Forest, and Artificial Neural Network (ANN) are applied. Our approach achieves a remarkable recall score ratio of 1.00, demonstrating high accuracy in Tor traffic identification. Notably, efficient feature selection has significantly reduced classification time. This work also contributes to effective Tor and non-Tor network traffic analysis, offering an efficient model for enhanced security and management.
  • EnsLearn: Leveraging Ensemble Learning for Online Encrypted Traffic Classification

    Gudla R., Vollala S., Amin R.

    Conference paper, 2024 15th International Conference on Computing Communication and Networking Technologies, ICCCNT 2024, 2024, DOI Link

    View abstract ⏷

    One of the most important tasks of effective network management is identifying and classifying traffic flows at the network level. Because encryption makes it difficult for network devices to identify the applications running. Existing techniques are likely to become ineffective in terms of performance because of the proliferated usage of encrypted communication. We propose a model called 'EnsLearn', that efficiently identifies encrypted traffic to address these challenges. This approach presents a technique that increase accuracy when applied to online encrypted traffic. Applications that run on the internet use reliable encryption methods to secure communication. These encryption techniques guarantee that no other party may reveal the data. As a result, this study determines whether traffic is encrypted or not. The zenodo dataset is used to train the model. The Wireshark application is used for collecting online data for testing. Initially, the dataset is divided into 64, 128, 256, and 512 KB files. Each one is segregated into binary, MP3, text, video, PDF, and image files. These files are converted into comma-separated values (CSV) for feature extraction using CICFlowmeter and apply preprocessing steps to make the dataset into compatible form. Next, dimensionality reduction techniques FastICA and IPCA are used for feature selection. Gradient Boosting, CatBoost, and AdaBoost are used for classification. Experiments show that the best results are achieved with the proposed approach CatBoost with dimensionality reduction technique IPCA as its classification model, where it achieves an accuracy of 99% in 0.10 seconds for encrypted traffic classification.
  • Reliable Network-Packet Binary Classification

    Gudla R., Vollala S., Amin R.

    Conference paper, Communications in Computer and Information Science, 2023, DOI Link

    View abstract ⏷

    A network packet identification and classification is a fundamental requirement of network management to maintain the quality of service, quality of experience, efficient bandwidth utilization, etc. This becomes increasingly significant in light of the Internet’s and online applications’ rapid expansion. With the advent of secure applications, more and more encrypted traffic is proliferated on the internet. Specifically, peer-to-peer applications with user-defined protocols severely affect network management. So there is necessary to identify and classify encrypted traffic in a network. To overcome this, our proposed approach network-packet binary classification is implemented to classify the network traffic as encrypted or compressed packets, with better classification accuracy and with the usage of a limited amount of classification time. To achieve this, our model uses a Decision tree classifier with one of the efficient feature selection methods, Autoencoder. Our experimental results show that our model outperforms the most state-of-the-art methods in terms of classification accuracy. Our model achieved 100% classification accuracy within 0.009 s of processing time.

Patents

Projects

Scholars

Interests

  • AI
  • Computer Networks
  • ML
  • Quantuam Communications
  • WSN

Thought Leaderships

There are no Thought Leaderships associated with this faculty.

Top Achievements

Research Area

No research areas found for this faculty.

Computer Science and Engineering is a fast-evolving discipline and this is an exciting time to become a Computer Scientist!

Computer Science and Engineering is a fast-evolving discipline and this is an exciting time to become a Computer Scientist!

Recent Updates

No recent updates found.

Education
2009
B.Tech
Kakatiya University, Warangal, Telangana
India
2014
M.Tech
JNTU Hyderabad
India
2025
PhD
IIIT Naya Raipur
India
Experience
  • SRM University-AP, Andhra Pradesh
  • Assistant Professor, Department of CSE, Sri Indu Institute of Engineering and Technology, Hyderabad, Telangana
  • Assistant Professor, Department of CSE, Vaagdevi Engineering College, Warangal Telangana
Research Interests
  • Computer Networks, AI, ML, Quantuam Communications, WSN
Awards & Fellowships
Memberships
  • Senior Member IEEE
Publications
  • TCC: Time constrained classification of VPN and non-VPN traffic using machine learning algorithms

    Gudla R., Vollala S., Srinivasa K.G., Amin R.

    Article, Wireless Networks, 2025, DOI Link

    View abstract ⏷

    Accurate traffic classification plays an important role in efficient utilization of network resources, quality of service, and overall management of the network. The identification of virtual private network (VPN) traffic, in particular, is important since it allows distinguishing between encrypted and non-encrypted traffic by VPN service, which is critical for security monitoring, traffic shaping, and the detection of possible misuse of network resources. VPNs are secure, encrypted connections over an insecure network with predetermined protocols; hence, through traditional methods, it is quite challenging to recognize the traffic pattern. This work introduces the time constrained classification (TCC) model, which use a decision tree classification algorithm with autoencoder dimensionality reduction to extract the key features from encrypted VPN traffic. The TCC model accurately classify VPN traffic from non-VPN traffic without degrading performance and limited amount of time. This approach optimizes the classification time for both binary and multi-class VPN and non-VPN traffic. Experimental results show that the decision tree-based autoencoder model achieves a recall score of 0.993 for multi-class classification in 1.8 s on the UNB ISCX VPN-nonVPN dataset (ISCXVPN2016), outperforming state-of-the-art methods while significantly reducing classification time.
  • Detectify: Leveraging Isolation Forest and K-Means for Optimized Network Traffic Anomaly Detection

    Gudla R., Vollala S., Ekka A., Ray S., Amin R.

    Conference paper, 2025 International Conference on Networks and Cryptology, NETCRYPT 2025, 2025, DOI Link

    View abstract ⏷

    Network security is the most essential aspect in today's world, that is, always being digitally connected, and being able to recognize abnormalities is important for defending against cyber attacks. Because regular security systems are not adequate for selective complex infiltrations, this often leads to the development of advanced machine learning models that will supplement the usual anomaly detection capabilities. Network intrusion has been evaluated using algorithms based on NSLKDD dataset that is commonly utilized as a yardstick. However, this study fills this gap, producing effective as well as reliable anomaly detection systems. We preprocessed the data in a comprehensive manner, chose features and used advanced methods like Isolation Forest, K-Means clustering, and Synthetic Minority Over-sampling Technique (SMOTE) in order to improve the quality of logistic regression, k-nearest neighbors and random forest performance through traditional models. Our findings prove much better in detection giving 99.33% accuracy. This means our proposed methodology is good at spotting threats and doing something about them. Application of Isolation Forest technique in anomalous traffic detection has brought unimaginable improvements in separating the two types of networks: legitimate one and malicious ones. The aforementioned is evidenced by our advanced models consistently outshining traditional methods, indicating that these techniques have the potential to strengthen network security against the growing threats of cybercrime through the amalgamation of K-Means clustering and SMOTE algorithms. Our sophisticated models have continued to surpass conventional methods, showcasing the versatility of these techniques in enhancing network security against emerging cyber threats.
  • A novel approach for classification of Tor and non-Tor traffic using efficient feature selection methods

    Gudla R., Vollala S., Srinivasa K.G., Amin R.

    Article, Expert Systems with Applications, 2024, DOI Link

    View abstract ⏷

    In the dynamic realm of encrypted communications, traffic analysis and its classification are crucial for efficient resource utilization and network management. The prevalence of encryption technologies, The Onion Router (Tor) a globally recognized privacy-preserving network, poses a challenge for the task at hand by introducing complexity through its innovative onion routing mechanism. To overcome Tor's limitations not only in terms of achieving better accuracy but also in performing classification in time-constrained scenarios, we propose a classification approach for Tor and non-Tor traffic classification, utilizing multiple models to enhance categorization and application identification. Leveraging the University of New Brunswick (UNB) Tor and non-Tor dataset, initially in a packet capture format, the preprocessing is done by transforming through CICFlowmeter. To expedite classification, we applied feature selection techniques like Principal Component Analysis (PCA) and t-Distributed Stochastic Neighbor Embedding (tSNE). Machine learning algorithms like support vector machine (SVM), Gradient Boosting, Random Forest, and Artificial Neural Network (ANN) are applied. Our approach achieves a remarkable recall score ratio of 1.00, demonstrating high accuracy in Tor traffic identification. Notably, efficient feature selection has significantly reduced classification time. This work also contributes to effective Tor and non-Tor network traffic analysis, offering an efficient model for enhanced security and management.
  • EnsLearn: Leveraging Ensemble Learning for Online Encrypted Traffic Classification

    Gudla R., Vollala S., Amin R.

    Conference paper, 2024 15th International Conference on Computing Communication and Networking Technologies, ICCCNT 2024, 2024, DOI Link

    View abstract ⏷

    One of the most important tasks of effective network management is identifying and classifying traffic flows at the network level. Because encryption makes it difficult for network devices to identify the applications running. Existing techniques are likely to become ineffective in terms of performance because of the proliferated usage of encrypted communication. We propose a model called 'EnsLearn', that efficiently identifies encrypted traffic to address these challenges. This approach presents a technique that increase accuracy when applied to online encrypted traffic. Applications that run on the internet use reliable encryption methods to secure communication. These encryption techniques guarantee that no other party may reveal the data. As a result, this study determines whether traffic is encrypted or not. The zenodo dataset is used to train the model. The Wireshark application is used for collecting online data for testing. Initially, the dataset is divided into 64, 128, 256, and 512 KB files. Each one is segregated into binary, MP3, text, video, PDF, and image files. These files are converted into comma-separated values (CSV) for feature extraction using CICFlowmeter and apply preprocessing steps to make the dataset into compatible form. Next, dimensionality reduction techniques FastICA and IPCA are used for feature selection. Gradient Boosting, CatBoost, and AdaBoost are used for classification. Experiments show that the best results are achieved with the proposed approach CatBoost with dimensionality reduction technique IPCA as its classification model, where it achieves an accuracy of 99% in 0.10 seconds for encrypted traffic classification.
  • Reliable Network-Packet Binary Classification

    Gudla R., Vollala S., Amin R.

    Conference paper, Communications in Computer and Information Science, 2023, DOI Link

    View abstract ⏷

    A network packet identification and classification is a fundamental requirement of network management to maintain the quality of service, quality of experience, efficient bandwidth utilization, etc. This becomes increasingly significant in light of the Internet’s and online applications’ rapid expansion. With the advent of secure applications, more and more encrypted traffic is proliferated on the internet. Specifically, peer-to-peer applications with user-defined protocols severely affect network management. So there is necessary to identify and classify encrypted traffic in a network. To overcome this, our proposed approach network-packet binary classification is implemented to classify the network traffic as encrypted or compressed packets, with better classification accuracy and with the usage of a limited amount of classification time. To achieve this, our model uses a Decision tree classifier with one of the efficient feature selection methods, Autoencoder. Our experimental results show that our model outperforms the most state-of-the-art methods in terms of classification accuracy. Our model achieved 100% classification accuracy within 0.009 s of processing time.
Contact Details

raju.gu@srmap.edu.in

Scholars
Interests

  • AI
  • Computer Networks
  • ML
  • Quantuam Communications
  • WSN

Education
2009
B.Tech
Kakatiya University, Warangal, Telangana
India
2014
M.Tech
JNTU Hyderabad
India
2025
PhD
IIIT Naya Raipur
India
Experience
  • SRM University-AP, Andhra Pradesh
  • Assistant Professor, Department of CSE, Sri Indu Institute of Engineering and Technology, Hyderabad, Telangana
  • Assistant Professor, Department of CSE, Vaagdevi Engineering College, Warangal Telangana
Research Interests
  • Computer Networks, AI, ML, Quantuam Communications, WSN
Awards & Fellowships
Memberships
  • Senior Member IEEE
Publications
  • TCC: Time constrained classification of VPN and non-VPN traffic using machine learning algorithms

    Gudla R., Vollala S., Srinivasa K.G., Amin R.

    Article, Wireless Networks, 2025, DOI Link

    View abstract ⏷

    Accurate traffic classification plays an important role in efficient utilization of network resources, quality of service, and overall management of the network. The identification of virtual private network (VPN) traffic, in particular, is important since it allows distinguishing between encrypted and non-encrypted traffic by VPN service, which is critical for security monitoring, traffic shaping, and the detection of possible misuse of network resources. VPNs are secure, encrypted connections over an insecure network with predetermined protocols; hence, through traditional methods, it is quite challenging to recognize the traffic pattern. This work introduces the time constrained classification (TCC) model, which use a decision tree classification algorithm with autoencoder dimensionality reduction to extract the key features from encrypted VPN traffic. The TCC model accurately classify VPN traffic from non-VPN traffic without degrading performance and limited amount of time. This approach optimizes the classification time for both binary and multi-class VPN and non-VPN traffic. Experimental results show that the decision tree-based autoencoder model achieves a recall score of 0.993 for multi-class classification in 1.8 s on the UNB ISCX VPN-nonVPN dataset (ISCXVPN2016), outperforming state-of-the-art methods while significantly reducing classification time.
  • Detectify: Leveraging Isolation Forest and K-Means for Optimized Network Traffic Anomaly Detection

    Gudla R., Vollala S., Ekka A., Ray S., Amin R.

    Conference paper, 2025 International Conference on Networks and Cryptology, NETCRYPT 2025, 2025, DOI Link

    View abstract ⏷

    Network security is the most essential aspect in today's world, that is, always being digitally connected, and being able to recognize abnormalities is important for defending against cyber attacks. Because regular security systems are not adequate for selective complex infiltrations, this often leads to the development of advanced machine learning models that will supplement the usual anomaly detection capabilities. Network intrusion has been evaluated using algorithms based on NSLKDD dataset that is commonly utilized as a yardstick. However, this study fills this gap, producing effective as well as reliable anomaly detection systems. We preprocessed the data in a comprehensive manner, chose features and used advanced methods like Isolation Forest, K-Means clustering, and Synthetic Minority Over-sampling Technique (SMOTE) in order to improve the quality of logistic regression, k-nearest neighbors and random forest performance through traditional models. Our findings prove much better in detection giving 99.33% accuracy. This means our proposed methodology is good at spotting threats and doing something about them. Application of Isolation Forest technique in anomalous traffic detection has brought unimaginable improvements in separating the two types of networks: legitimate one and malicious ones. The aforementioned is evidenced by our advanced models consistently outshining traditional methods, indicating that these techniques have the potential to strengthen network security against the growing threats of cybercrime through the amalgamation of K-Means clustering and SMOTE algorithms. Our sophisticated models have continued to surpass conventional methods, showcasing the versatility of these techniques in enhancing network security against emerging cyber threats.
  • A novel approach for classification of Tor and non-Tor traffic using efficient feature selection methods

    Gudla R., Vollala S., Srinivasa K.G., Amin R.

    Article, Expert Systems with Applications, 2024, DOI Link

    View abstract ⏷

    In the dynamic realm of encrypted communications, traffic analysis and its classification are crucial for efficient resource utilization and network management. The prevalence of encryption technologies, The Onion Router (Tor) a globally recognized privacy-preserving network, poses a challenge for the task at hand by introducing complexity through its innovative onion routing mechanism. To overcome Tor's limitations not only in terms of achieving better accuracy but also in performing classification in time-constrained scenarios, we propose a classification approach for Tor and non-Tor traffic classification, utilizing multiple models to enhance categorization and application identification. Leveraging the University of New Brunswick (UNB) Tor and non-Tor dataset, initially in a packet capture format, the preprocessing is done by transforming through CICFlowmeter. To expedite classification, we applied feature selection techniques like Principal Component Analysis (PCA) and t-Distributed Stochastic Neighbor Embedding (tSNE). Machine learning algorithms like support vector machine (SVM), Gradient Boosting, Random Forest, and Artificial Neural Network (ANN) are applied. Our approach achieves a remarkable recall score ratio of 1.00, demonstrating high accuracy in Tor traffic identification. Notably, efficient feature selection has significantly reduced classification time. This work also contributes to effective Tor and non-Tor network traffic analysis, offering an efficient model for enhanced security and management.
  • EnsLearn: Leveraging Ensemble Learning for Online Encrypted Traffic Classification

    Gudla R., Vollala S., Amin R.

    Conference paper, 2024 15th International Conference on Computing Communication and Networking Technologies, ICCCNT 2024, 2024, DOI Link

    View abstract ⏷

    One of the most important tasks of effective network management is identifying and classifying traffic flows at the network level. Because encryption makes it difficult for network devices to identify the applications running. Existing techniques are likely to become ineffective in terms of performance because of the proliferated usage of encrypted communication. We propose a model called 'EnsLearn', that efficiently identifies encrypted traffic to address these challenges. This approach presents a technique that increase accuracy when applied to online encrypted traffic. Applications that run on the internet use reliable encryption methods to secure communication. These encryption techniques guarantee that no other party may reveal the data. As a result, this study determines whether traffic is encrypted or not. The zenodo dataset is used to train the model. The Wireshark application is used for collecting online data for testing. Initially, the dataset is divided into 64, 128, 256, and 512 KB files. Each one is segregated into binary, MP3, text, video, PDF, and image files. These files are converted into comma-separated values (CSV) for feature extraction using CICFlowmeter and apply preprocessing steps to make the dataset into compatible form. Next, dimensionality reduction techniques FastICA and IPCA are used for feature selection. Gradient Boosting, CatBoost, and AdaBoost are used for classification. Experiments show that the best results are achieved with the proposed approach CatBoost with dimensionality reduction technique IPCA as its classification model, where it achieves an accuracy of 99% in 0.10 seconds for encrypted traffic classification.
  • Reliable Network-Packet Binary Classification

    Gudla R., Vollala S., Amin R.

    Conference paper, Communications in Computer and Information Science, 2023, DOI Link

    View abstract ⏷

    A network packet identification and classification is a fundamental requirement of network management to maintain the quality of service, quality of experience, efficient bandwidth utilization, etc. This becomes increasingly significant in light of the Internet’s and online applications’ rapid expansion. With the advent of secure applications, more and more encrypted traffic is proliferated on the internet. Specifically, peer-to-peer applications with user-defined protocols severely affect network management. So there is necessary to identify and classify encrypted traffic in a network. To overcome this, our proposed approach network-packet binary classification is implemented to classify the network traffic as encrypted or compressed packets, with better classification accuracy and with the usage of a limited amount of classification time. To achieve this, our model uses a Decision tree classifier with one of the efficient feature selection methods, Autoencoder. Our experimental results show that our model outperforms the most state-of-the-art methods in terms of classification accuracy. Our model achieved 100% classification accuracy within 0.009 s of processing time.
Contact Details

raju.gu@srmap.edu.in

Scholars